The Ultimate Guide to Security Information and Event Management
A curated Australian edition of IndustrialDay news, analysis, interviews, reviews, job moves, and related resources for Security Information and Event Management (SIEM).
What to know about Security Information and Event Management
Security Information and Event Management (SIEM) is a critical component in the cybersecurity landscape, combining real-time analysis of security alerts with centralized data collection to enable effective threat detection, incident response, and compliance management. As cyber threats grow increasingly sophisticated, SIEM platforms have evolved, integrating advanced analytics, artificial intelligence, and cloud capabilities to help organizations stay ahead of attacks.
This tag gathers stories highlighting the ongoing developments and challenges within the SIEM domain, including strategic considerations for security frameworks, innovative product launches, key acquisitions, and partnerships from notable vendors. Readers will find insights into how AI and machine learning are transforming SIEM functionalities, addressing skills shortages, and automating incident response to enhance security operations centers' efficiency.
Additionally, these articles explore the market dynamics of SIEM solutions, from emerging technologies and vendor comparisons to practical guidance on implementing, optimizing, and managing SIEM platforms. Whether you are an IT security professional seeking the latest trends or a business leader aiming to understand the role of SIEM in cyber risk management, this collection offers valuable perspectives to inform your cybersecurity strategy.
Australian Security Information and Event Management News
Regional stories with direct local relevance
Nozomi launches Compass for OT asset & service management
Industrial operators will get faster compliance evidence and safer change control as the new platform replaces spreadsheets and manual OT workflows in January.
VAST Data & CrowdStrike widen AI security integration
Security teams could gain wider visibility into AI data flows as native Falcon support and two CrowdStrike integrations extend across VAST's platform.
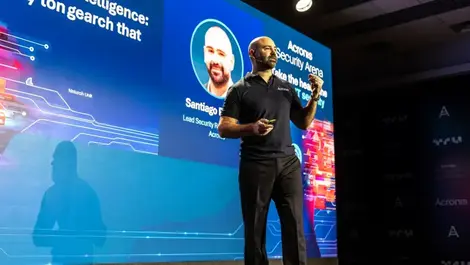
Acronis says frontier AI is speeding cyber attacks
Frontier AI is lowering the bar for cybercrime, with attackers using it to scale phishing, malware and reconnaissance more quickly.

Macquarie Government launches Azure practice for agencies
Australian agencies can now tap managed Azure services as Macquarie Government broadens its cloud offer amid pressure to modernise securely and cut costs.

Australian firms turn to unified security platforms
Rising alert volumes and AI-driven threats are pushing Australian organisations towards unified security platforms, a Fortinet study found.

The real cost of build vs. buy for agentic AI in regulated banking
Banks risk repeating DevOps sprawl as DIY agentic AI pushes build costs above USD $1.4 million and delays production by up to 18 months.
Analyst Insights
Research and market analysis connected to Security Information and Event Management
Thrive bolsters NextGen platform with Elastic, Cato

F5 expands AI Gateway to curb costs & secure agents

Jamf launches AI governance for Mac as usage rises

Jamf launches AI governance for Mac fleets in enterprises
Fortinet launches FortiSOC cloud security platform
Featured News

Expert Columns
When AI memory, simulation and provenance collide
The real cost of build vs. buy for agentic AI in regulated banking

What Swiss Cheese teaches us about choosing MDR

The evolving role of the CSO: From technical guardian to business strategist
Why AI-powered security needs network telemetry across the hybrid cloud
Observability & AI spark Australia's business edge
Why agentic AI is the game-changer SOCs need

Why now is the time to modernise your SIEM
Interviews
Interviews and video coverage from the network
Recent Security Information and Event Management News
BeyondTrust links privilege data to CrowdStrike Falcon
Joint customers can now spot privileged identity risks alongside threat alerts in CrowdStrike Falcon, after BeyondTrust added new data feeds.
BlueVoyant launches Microsoft Defender XDR ISOC service
The service is aimed at firms that pay for Microsoft security tools but have yet to turn them into fully operational defences.
Gravwell unveils five AI agents for security teams
Security teams can now use narrowly scoped agents to triage alerts, investigate cases and check systems without giving AI unrestricted access.
AI agents top insider risk concern for security chiefs
Surveyed firms are struggling to spot when autonomous tools stray from approved tasks, as 48% of security leaders now rank them as their biggest insider threat.
Mandiant warns of AI agents fuelling new attack risks
Autonomous systems are now creating fresh avenues for code theft, remote execution and runaway cloud spending, Mandiant says.
Horizon3 links NodeZero to CrowdStrike Falcon SIEM
Security teams can now compare validated exposure findings with endpoint and cloud telemetry after Horizon3 tied NodeZero into CrowdStrike's SIEM.
AI agents now seen as biggest insider risk, Exabeam
Nearly half of security leaders now rank AI agents above external hackers and malicious insiders, according to Exabeam's survey.
Eventus Security urges decision-centric SOCs at AI summit
Growing alert volumes are pushing Indian security teams to use AI for faster, context-led decisions instead of more monitoring.
Filigran adds attack chaining to OpenAEV v3 release
Security teams can now trace how one weak point becomes a full breach path as Filigran automates multi-step testing in OpenAEV v3.
CrowdStrike launches SafeMind and cyber defence AI lab
Enterprise security teams could see faster breach detection and response as CrowdStrike's new AI models are trained on live threat data.
ClickHouse buys RunReveal to boost security analytics
Security teams could get faster investigations as ClickHouse folds RunReveal's platform expertise into its database business.
Commvault links recovery actions into CrowdStrike SOAR
Joint users can now automate cyber recovery steps during incidents, cutting handoffs and helping preserve clean backup points for ransomware response.
CrowdStrike launches Falcon IQ to automate AI defence
Customers will get real-time remediation tracking as CrowdStrike adds automation and new data links to its AI defence coalition.
Exabeam named Google Unified Security partner for analytics
Security teams could spot insider threats sooner as Exabeam joins Google's recommended partner programme for behavioural analytics tied to AI agents.
ExtraHop launches 400 Gbps sensor for RevealX platform
It aims to close a visibility gap for security teams as enterprise data centres outpace 100 Gbps tools and AI traffic surges.
ConnectWise opens Australian data centre for x360Recover
APAC partners can now keep backup data in Australia, easing sovereignty concerns and cutting recovery delays for regulated customers.
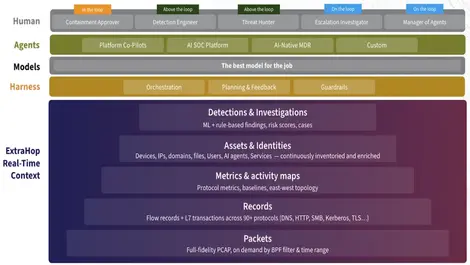
ExtraHop launches 400 Gbps sensor for RevealX platform
Security teams face wider blind spots as ExtraHop's new sensor brings full inspection of 400 Gbps data centre traffic to RevealX.
Australian tech leaders urge cyber recovery planning
Rising AI-driven attacks are forcing businesses to test recovery plans before breaches hit, executives say, as minutes now matter.
ReliaQuest deepens Anthropic deal to bolster GreyMatter
GreyMatter users will gain wider access to Anthropic's Claude models as ReliaQuest brings them deeper into its threat response platform.
SonicWall launches endpoint security service for MSP market
Smaller businesses could gain cheaper ransomware protection as managed service providers get a new endpoint security option from SonicWall.